India’s Leading SSL Certificate Provider
 Login


RapidSSL SSL and Digital Certificates
Streamlined domain validated TLS for teams that prioritise straightforward HTTPS deployment, with single domain, Wildcard and automated lifecycle options for supported environments.
Choosing the
Right RapidSSL Certificate
Start with validation, domain architecture and lifecycle requirements.
Streamlined domain validated TLS for teams that prioritise straightforward
Brand
Security
Customer Trust
Your Business
RapidSSL Certificate Families
Understand the portfolio before comparing individual products.
RapidSSL Core Certificates
DV certificate for eligible subdomains under one base domain, suited to teams that want simpler certificate coverage without managing each subdomain separately.
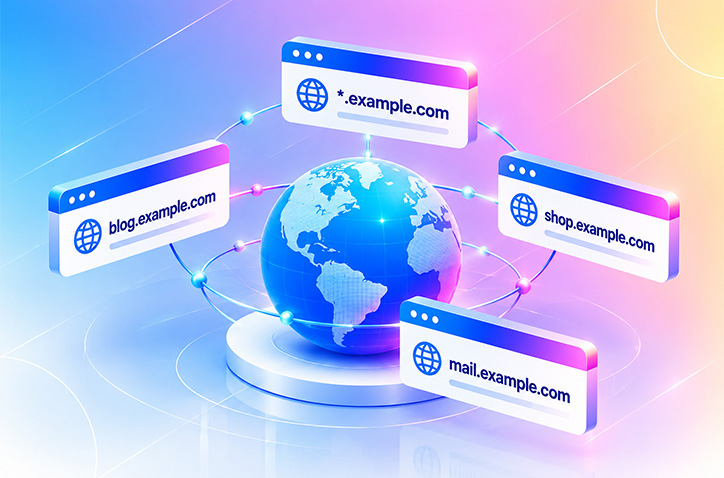
Wildcard and Multi Domain
Use these products when the environment extends beyond one stable hostname and requires subdomain or named domain coverage.
Management and Automation
Where available, flexible or automated products can reduce manual certificate administration across supported systems.
Compare RapidSSL Products
Concise product summaries keep the catalogue scannable. Open a product page for detailed specifications, buyer guidance, use cases and FAQs.

RapidSSL Wildcard Plan + Automate
Affordable wildcard HTTPS with automated certificate management
RapidSSL Plan + Automate
Simplify HTTPS with automated issuance, installation and renewal
RapidSSL Wildcard Certificate
Secure a single domain and multiple subdomains quickly and economically
RapidSSL Certificate
Enable HTTPS quickly with an affordable single-domain certificate
RapidSSL Wildcard Plan + Automate
Affordable wildcard HTTPS with automated certificate management
RapidSSL Plan + Automate
Simplify HTTPS with automated issuance, installation and renewal
RapidSSL Wildcard Certificate
Secure a single domain and multiple subdomains quickly and economically
RapidSSL Certificate
Enable HTTPS quickly with an affordable single-domain certificate
RapidSSL Wildcard Plan + Automate
Affordable wildcard HTTPS with automated certificate management
RapidSSL Wildcard Certificate
Secure a single domain and multiple subdomains quickly and economically
Where RapidSSL Certificates Can Fit
Explore illustrative use cases showing how certificate solutions can support diverse digital environments and industry requirements.
Public digital services
Startups teams can use RapidSSL products where the selected validation level and domain architecture match customer facing websites, portals or APIs.
Measure certificate administration time, renewal events and service interruptions caused by expiry or configuration errors.
Application and portal estate
For MSME, the certificate choice should follow the number of domains, subdomain pattern, identity assurance requirement and private key ownership model.
Measure domain onboarding lead time, validation workload and the operational impact of certificate consolidation.
Certificate lifecycle governance
Marketing Websites organisations with several certificates should define inventory, accountable owners, expiry monitoring, reissue procedures and automation where supported.
Measure inventory accuracy, renewal success rate, exception handling and engineer effort spent on certificate lifecycle tasks.
Public digital services
Education teams can use RapidSSL products where the selected validation level and domain architecture match customer facing websites, portals or APIs.
Measure certificate administration time, renewal events and service interruptions caused by expiry or configuration errors.
RapidSSL FAQ
Real buyer questions covering selection, validation, deployment and lifecycle.
Start with the required validation and hostname structure, then compare suitable RapidSSL products. Do not choose only by price or warranty.
Yes where the selected RapidSSL product supports Multi Domain, SAN or FLEX coverage. Confirm the exact current SKU capacity before ordering.
The RapidSSL catalogue includes wildcard capable products where shown. Confirm the exact wildcard pattern and whether additional base domains are required.
Yes, provided the selected product matches the organisation validation, domain architecture, platform and lifecycle requirement.
Compare validation, domain coverage, current warranty, support, management features, reissue rules, automation and total operational fit.
Use a single site certificate for a stable hostname. Consider Wildcard when several eligible first level subdomains share one base domain and the private key architecture is acceptable.
Many products allow deployment or reissue according to current licensing rules. Confirm the exact product terms and protect the private key during any migration.
The certificate authority verifies domain control and organisation identity using its current validation procedures. Exact evidence can vary by product and organisation type.
Domain validation can often complete quickly when domain control is available. Organisation and extended validation depend on successful identity checks, so issuance time should be treated as conditional rather than guaranteed.
Often yes when the architecture and licence permit it. Confirm where TLS terminates, how the key is stored and whether the same trust boundary should span all endpoints.
Treat the certificate as compromised, revoke or replace it as appropriate, generate a new protected key and investigate how the exposure occurred.
No. A site seal is a visible trust element offered with some products. The underlying certificate validation and TLS connection are separate.
It can be highly automated on supported platforms and products, but monitoring, ownership and failure handling are still necessary.
Assign accountable owners by application or platform, maintain a central inventory, define key handling rules, monitor expiry and document reissue and revocation procedures.
Public certificate support for IP addresses depends on current certificate authority policy and product capability. Verify the exact requirement before purchase.
Only after assessing the trust boundary. Broad key reuse can simplify deployment but increases exposure if one server is compromised.
Confirm the exact hostnames, validation category, wildcard pattern, SAN count, server platform, key ownership, lifecycle process and current commercial specifications.
Support varies by seller and product. NTSPL can provide selection and deployment assistance, while the certificate itself should not be confused with a managed security service.
Some products support changes through reissue or flexible domain configuration within current rules. Verify the selected product before planning frequent hostname changes.
Use a central inventory, responsible owner, multiple expiry alerts, tested renewal procedures and automation where appropriate. Do not rely on a single email reminder.